
Implementing Secure Authentication Systems in Modern Web Applications
In the digital era, secure authentication is paramount for protecting user information and ensuring that only authorized users gain access to sensitive data. This blog post explores how to implement robust authentication systems in modern web applications, focusing on best practices and secure code examples to help you prevent vulnerabilities and protect user credentials.
1. Understanding the Basics of Authentication
Authentication is the process of verifying the identity of a user or system. This typically involves checking credentials like usernames and passwords against a stored database. Secure authentication adds layers of protection, such as hashing passwords, using salts, and adopting modern protocols like OAuth2 or JWT (JSON Web Tokens).
For example, hashing is crucial for storing passwords. Below is a Python snippet using bcrypt:
import bcrypt

def hash_password(password):
  # Generate a salt
  salt = bcrypt.gensalt()
  # Hash the password
  hashed = bcrypt.hashpw(password.encode('utf-8'), salt)
  return hashed.decode('utf-8')

plain_pass = 'secure_password'
hashed_pass = hash_password(plain_pass)
print('Hashed Password:', hashed_pass)
Bcrypt provides an adaptive hashing algorithm, making it computationally intensive to brute force passwords.
2. Implementing OAuth 2.0
OAuth 2.0 is a standard for delegated authorization, enabling third-party applications to obtain limited access to user accounts. Implementing OAuth involves setting up an authorization server and generating access tokens. Here’s a simple example demonstrating OAuth 2.0 implementation in Node.js:
const express = require('express');
const jwt = require('jsonwebtoken');

const app = express();
const port = 3000;
app.use(express.json());

app.post('/token', (req, res) => {
  const { username, password } = req.body;
  if (username === 'admin' && password === 'password') {
    const token = jwt.sign({ username }, 'secret_key', { expiresIn: '1h' });
    res.json({ accessToken: token });
  } else {
    res.sendStatus(401);
  }
});

app.listen(port, () => {
  console.log(`Auth server running at http://localhost:${port}`);
});
Ensure to manage secret keys properly and never hardcode them in production code. Environment variables or secure vaults offer a better alternative.
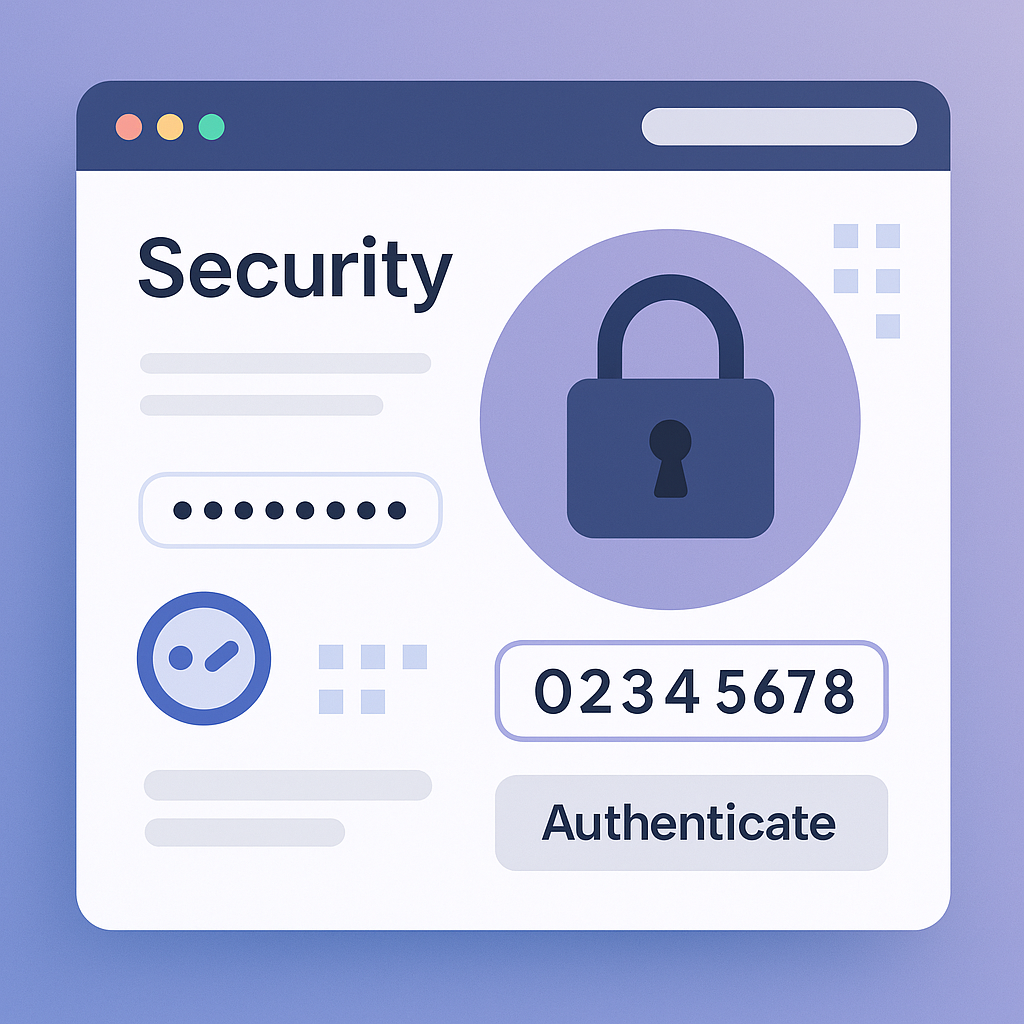
3. Multi-Factor Authentication (MFA)
MFA enhances security by requiring more than one form of verification. Common methods include SMS codes, authenticator apps, or hardware tokens. For example, integrating Google Authenticator using the speakeasy package in Node.js:
const speakeasy = require('speakeasy');

// Generate a secret key
const secret = speakeasy.generateSecret({ length: 20 });
console.log('Secret:', secret.base32);

// Verify a user-provided token
const verified = speakeasy.totp.verify({
  secret: secret.base32,
  encoding: 'base32',
  token: '123456'
});
console.log('Verified:', verified);
Using MFA significantly reduces the risk of unauthorized access due to compromised passwords.
4. Implementing Rate Limiting
Rate limiting is a defense against brute force attacks and resource abuse. By restricting the number of authentication requests, you can prevent attackers from guessing credentials at high speed. Here’s a basic implementation using express-rate-limit in Node.js:
const rateLimit = require('express-rate-limit');

const limiter = rateLimit({
  windowMs: 15 * 60 * 1000, // 15 minutes
  max: 100 // limit each IP to 100 requests per windowMs
});

app.use(limiter);
Rate limiting improves application performance and security by throttling potentially harmful requests.
5. Logging and Monitoring
Continuous logging and monitoring of authentication requests help to detect and respond to potential threats swiftly. Logging in Node.js could be as basic as using the Winston library:
const winston = require('winston');

const logger = winston.createLogger({
  level: 'info',
  format: winston.format.json(),
  transports: [
    new winston.transports.File({ filename: 'combined.log' })
  ]
});

logger.info('Auth request received');
Ensure your logs are properly secured and analyze them regularly for suspicious activities.
In conclusion, building secure authentication systems involves implementing multiple layers of protection, using modern libraries and protocols, and continuously monitoring system activities. These practices, combined with user education and regular updates, will strengthen your web application’s security posture and safeguard user data.
Useful links: